


How to Enable Two-Factor Authentication for All Users in Lucidya
Learn how administrators can enable, edit, and disable Two-Factor Authentication for all users in Lucidya, including Email, SMS, and Authenticator App verification methods.
Two-Factor Authentication (2FA) adds an extra security layer to your organization's Lucidya account by requiring users to verify their identity with a one-time password each time they log in. Once enabled by an administrator, all users must complete 2FA setup at their next login.
Before You Start
You need Manager permission for the General Settings module to enable, edit, or disable 2FA for your organization.
Access Two-Factor Authentication Page
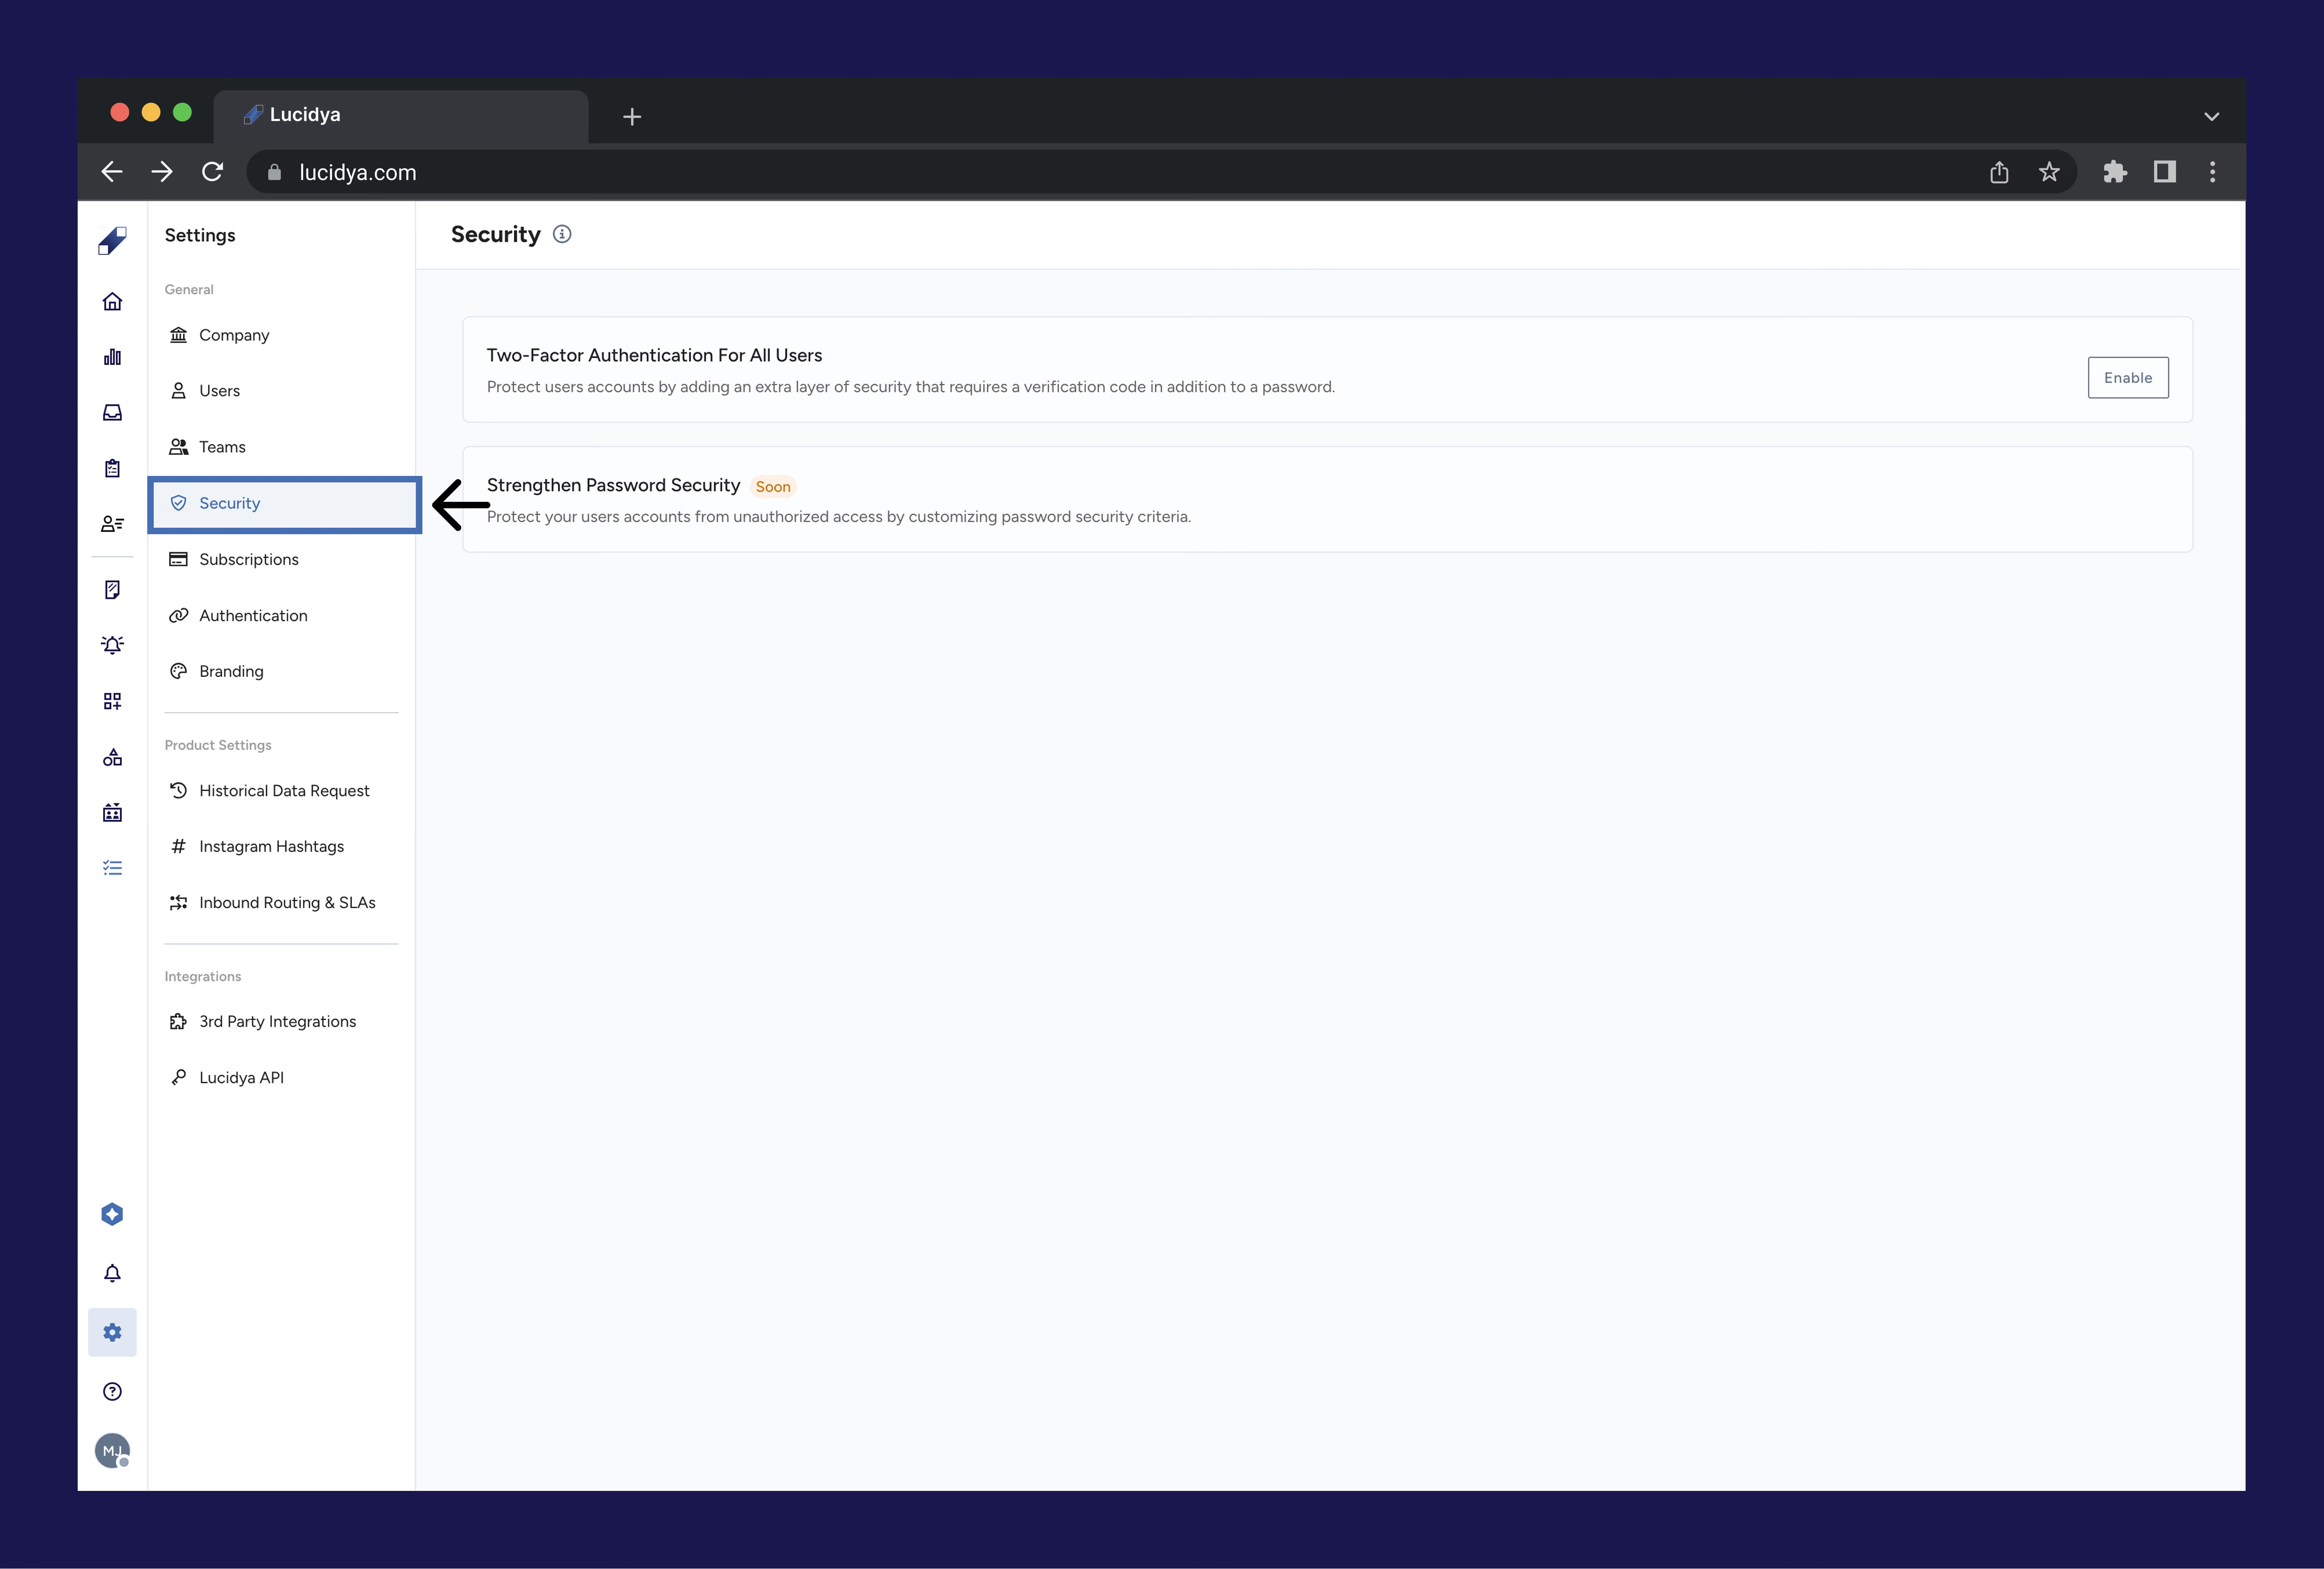
- Click the Settings icon in the left sidebar. You must have Manager permission for the General Settings module.
- On the Settings page, click the Security tab.
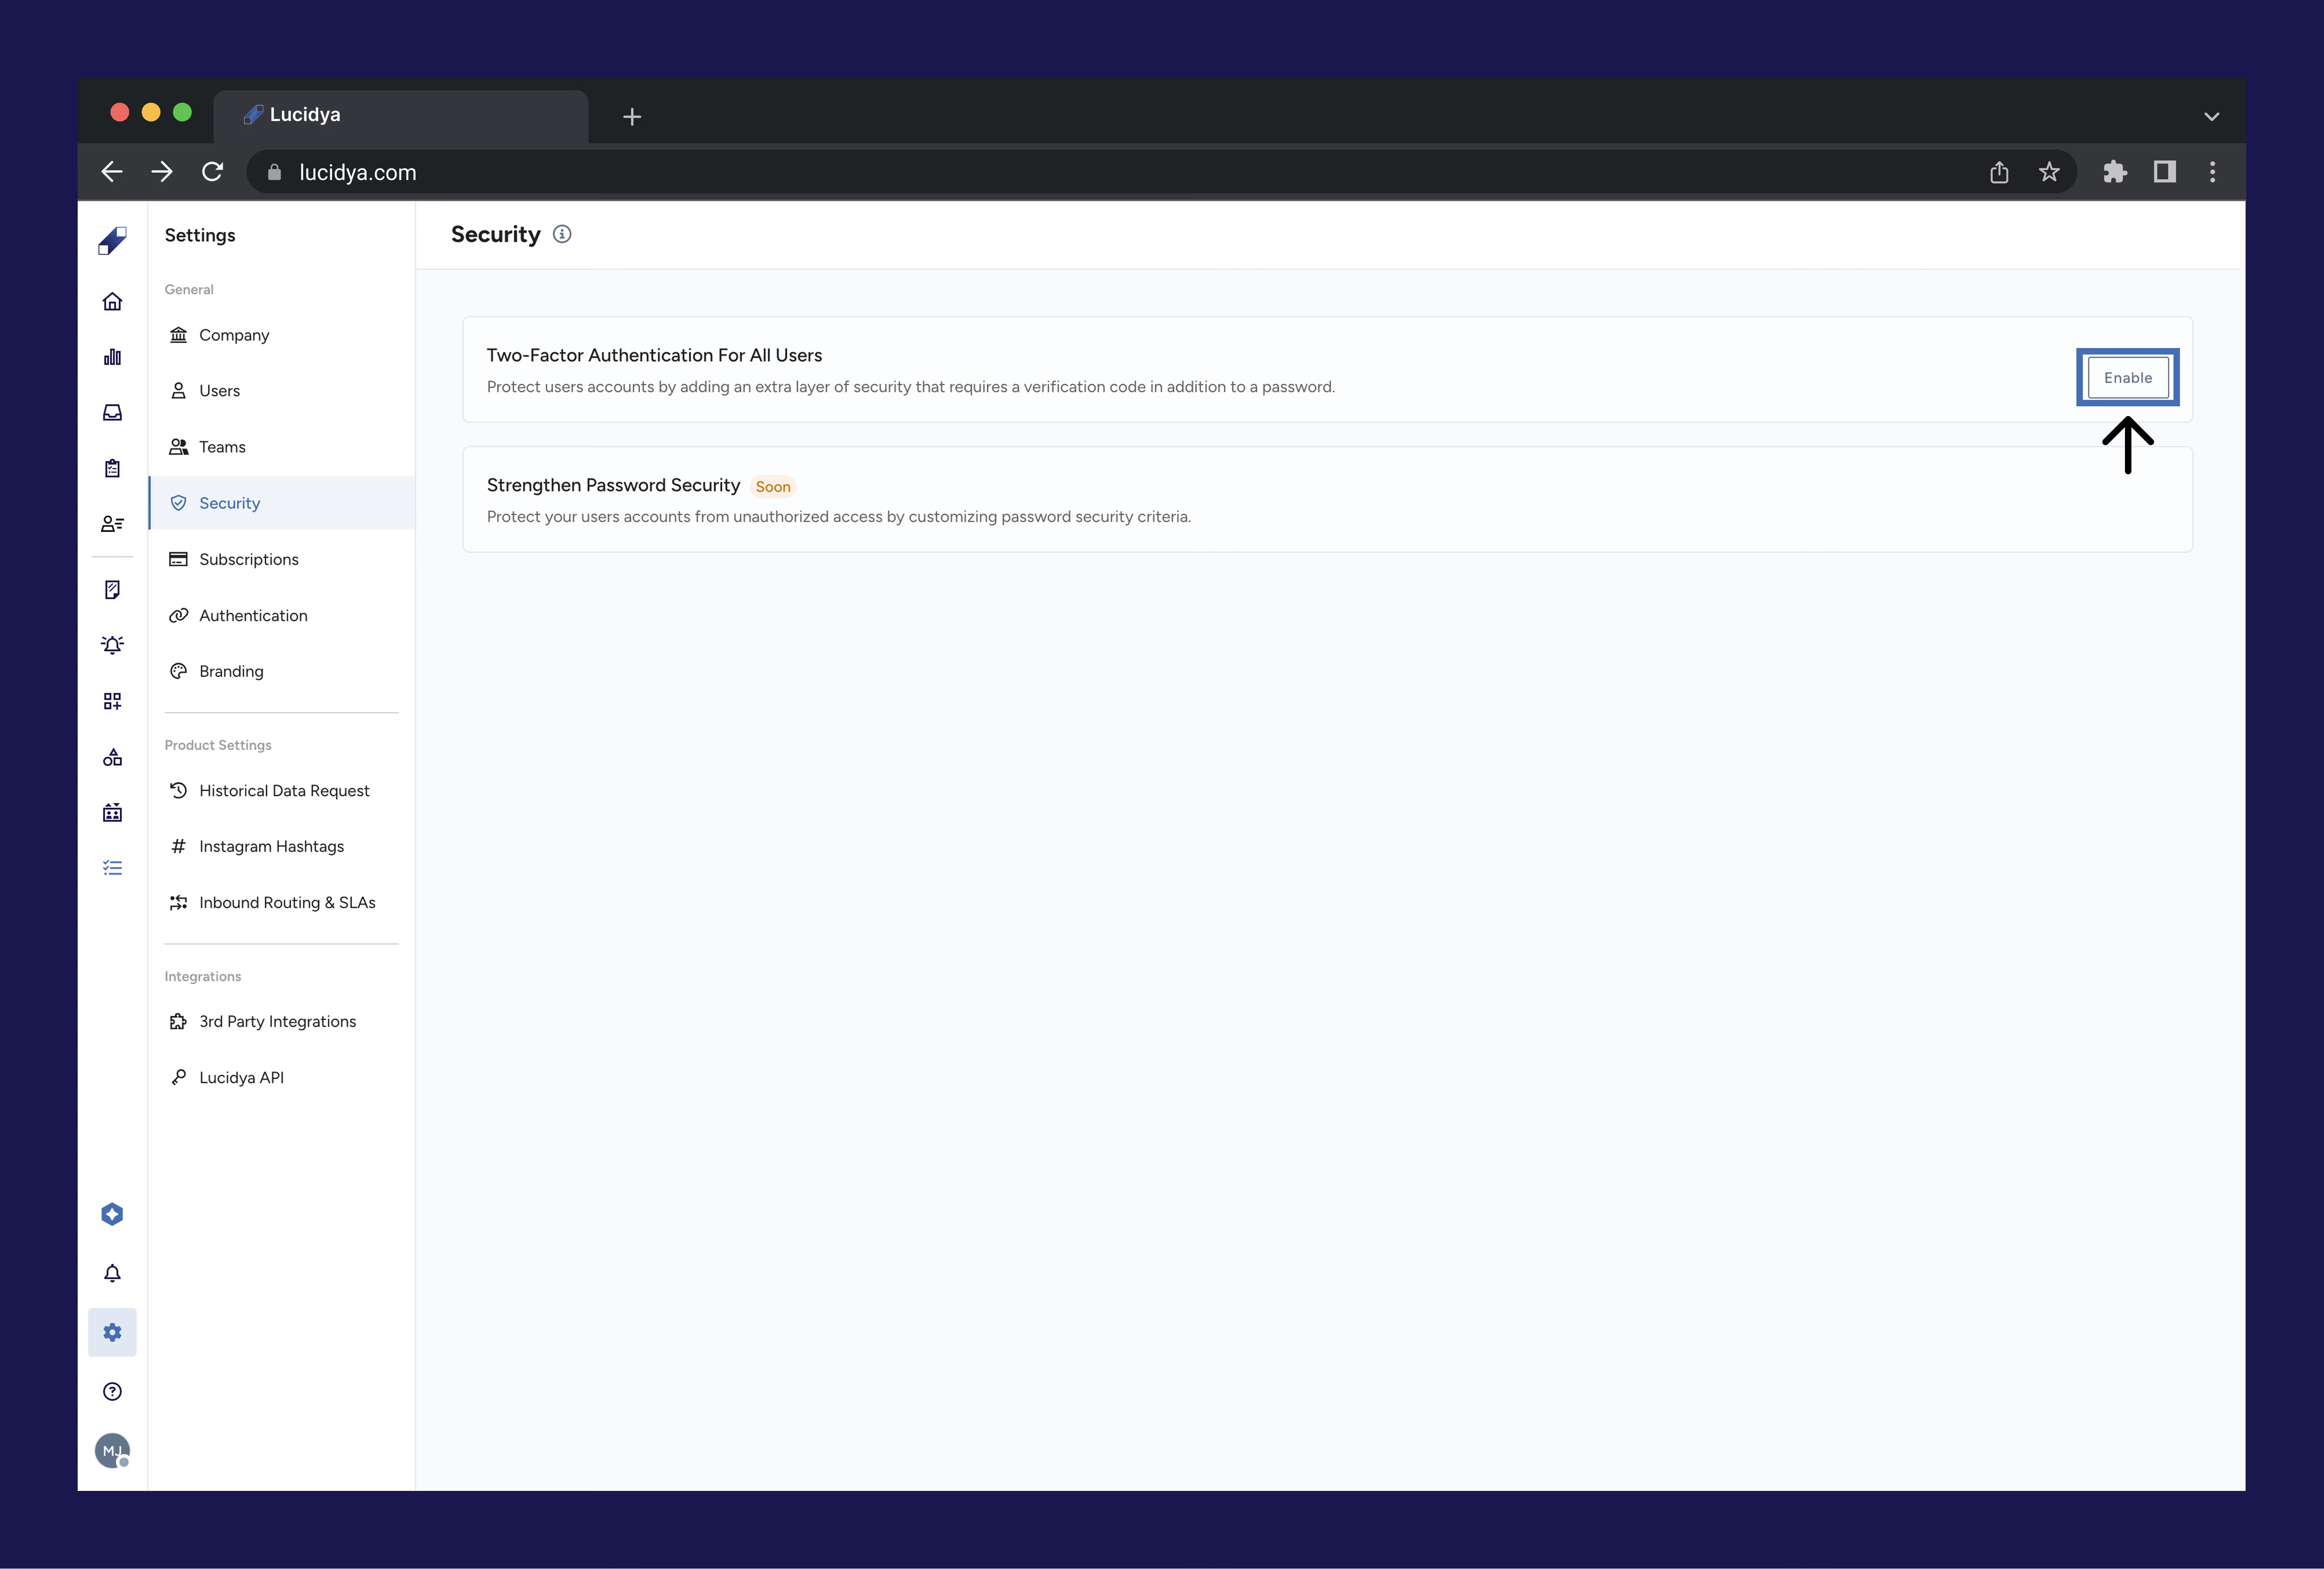
- Click the Enable button under Two-Factor Authentication For All Users.

Step 1. Access the Security Settings
- Click the Settings icon in the left sidebar.
- On the Settings page click the Security tab.
- Click the Enable button under Two-Factor Authentication For All Users.
Step 2. Select Verification Methods
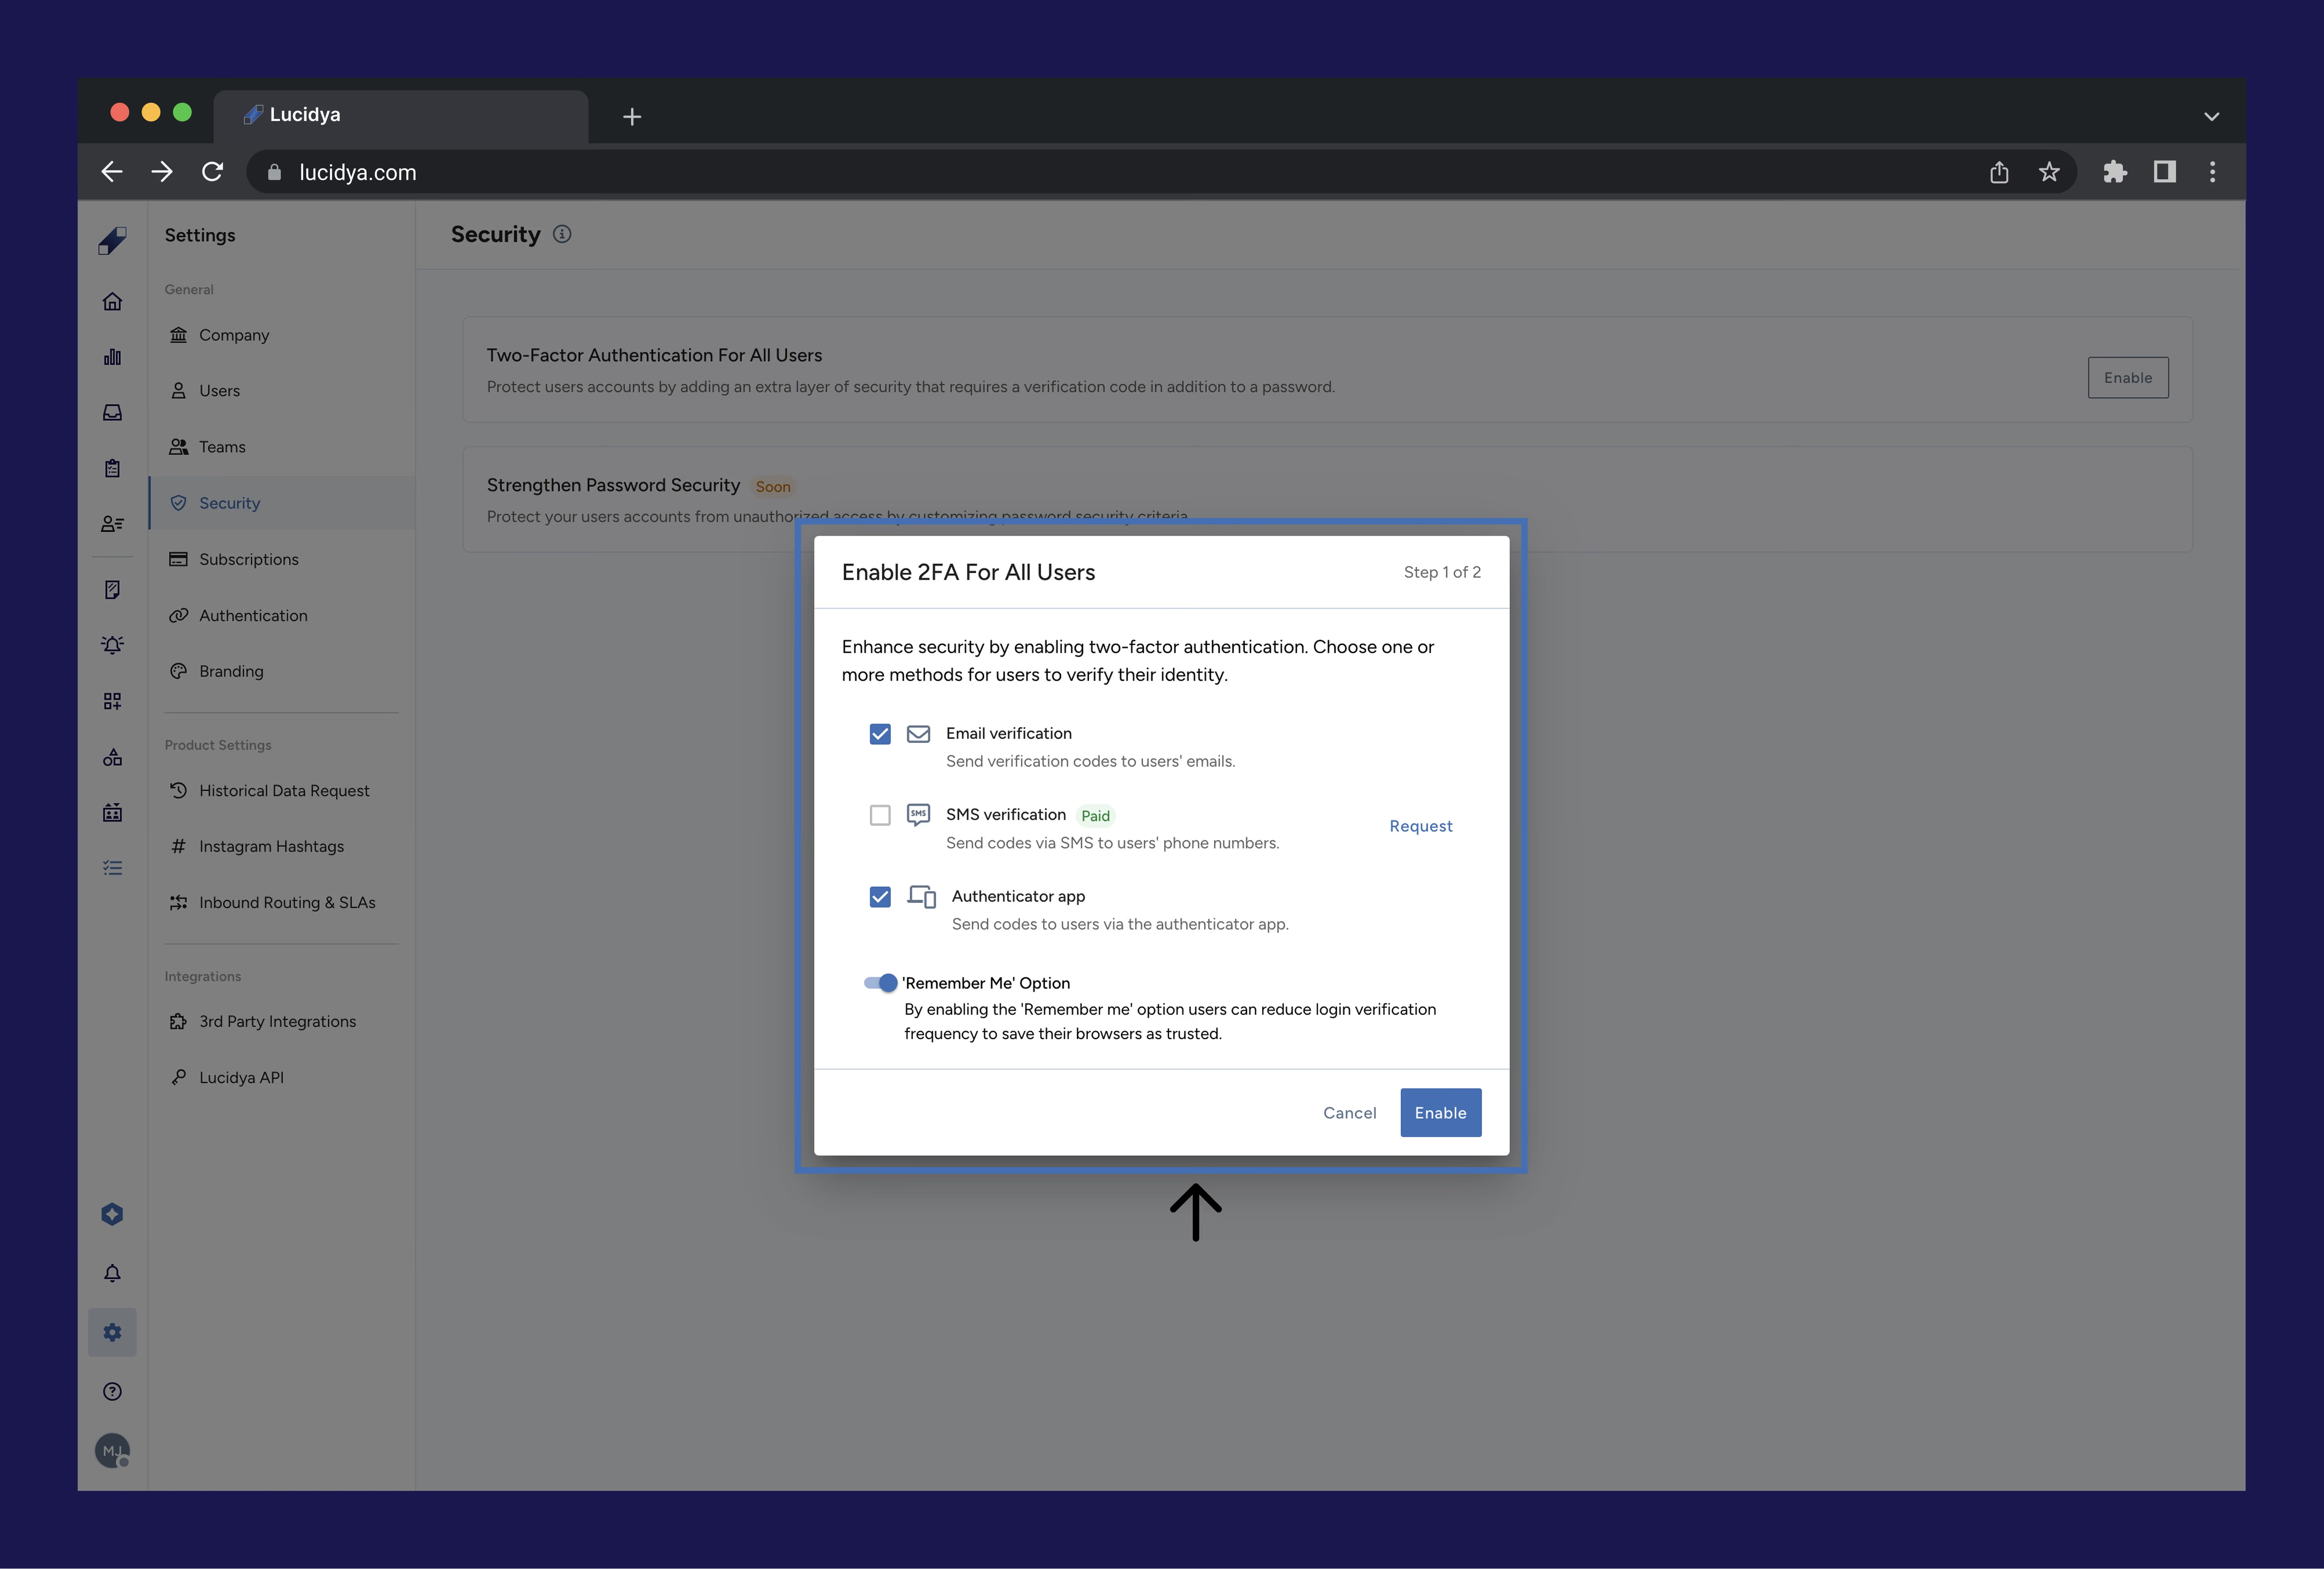
A popup will appear. Select at least one verification method to make available to your users. The Enable button remains inactive until at least one method is selected.
- Email Verification: sends a one-time code to the user's email address. Available on all packages.
- SMS Verification: sends a one-time code via SMS to the user's phone number. This is a paid add-on and requires the SMS package. If your account doesn't include it, a Paid label appears next to the SMS option with a Request button. Clicking Request changes the button to Requested and becomes non-clickable. A confirmation snackbar appears, and a notification is sent to the Customer Success team.
- Authenticator App: users verify through an authenticator app such as Google Authenticator or Microsoft Authenticator. Available on all packages.
Step 3. Configure Remember Device (Optional)
A Remember Device toggle is available and is off by default. When enabled, users will see a "Don't ask again for 7 days" checkbox on the login screen that lets them skip 2FA verification on that browser for 7 days.
Click Enable to proceed.
Step 4. Complete Your Own Verification
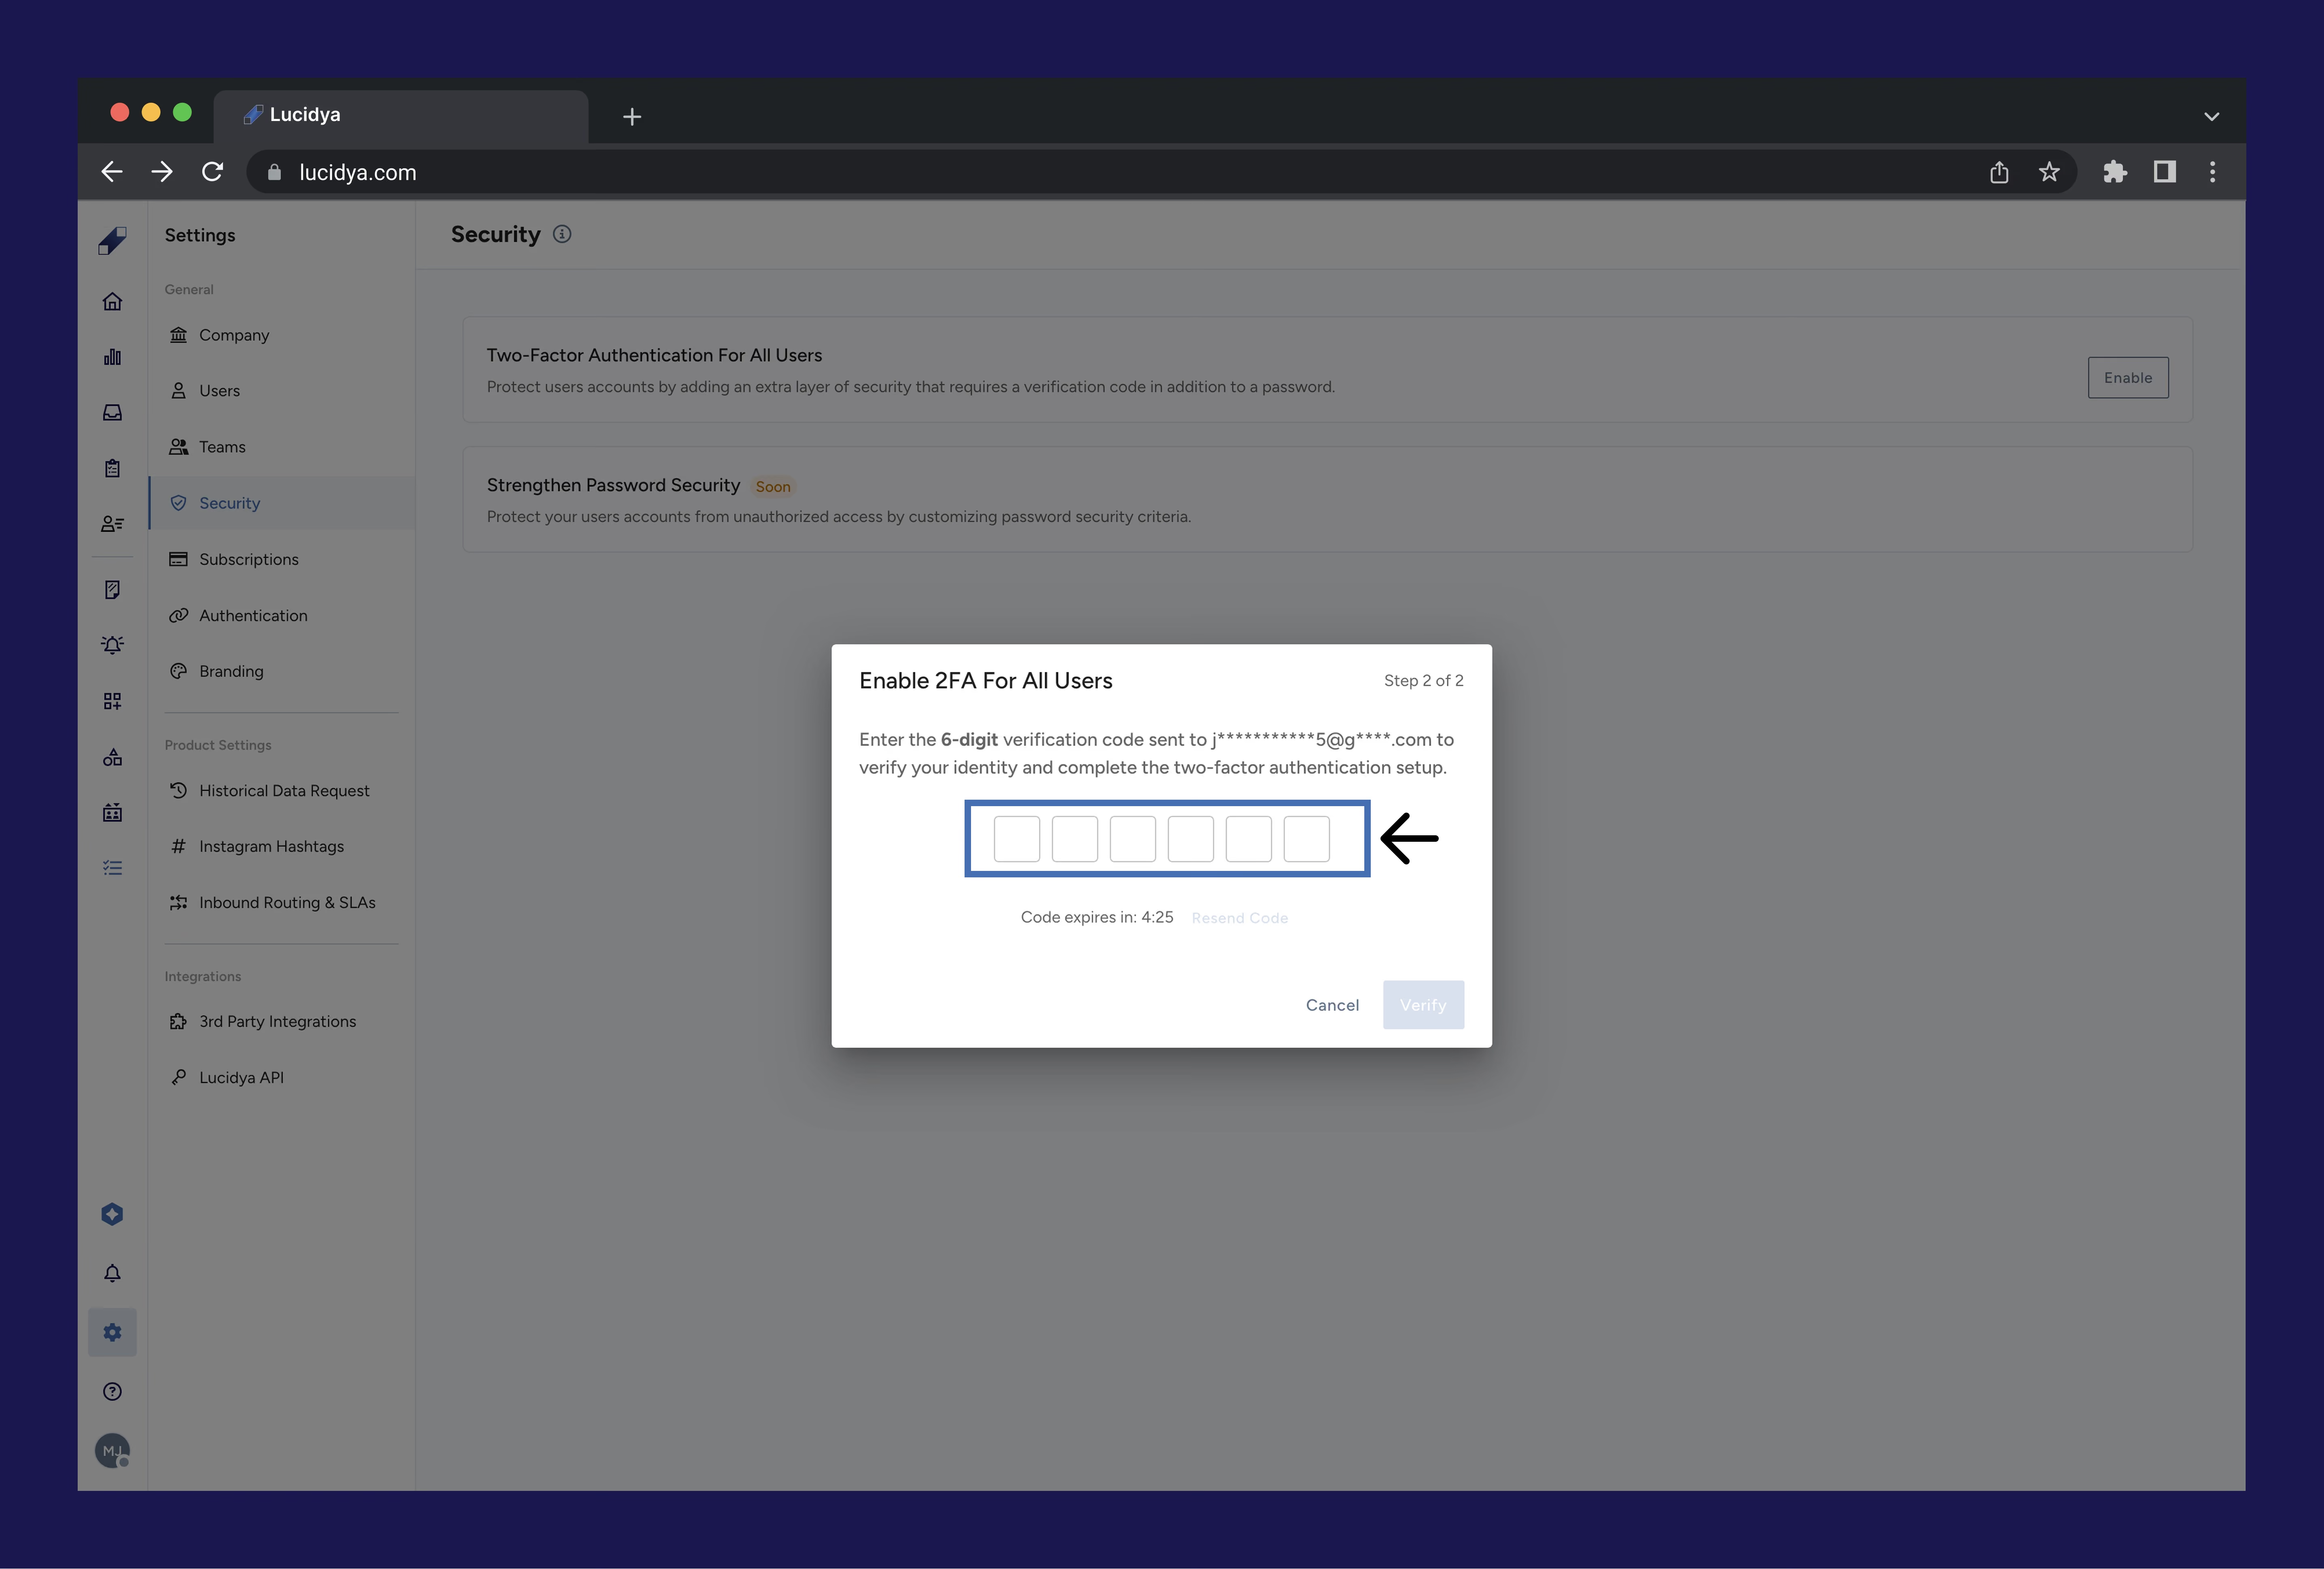
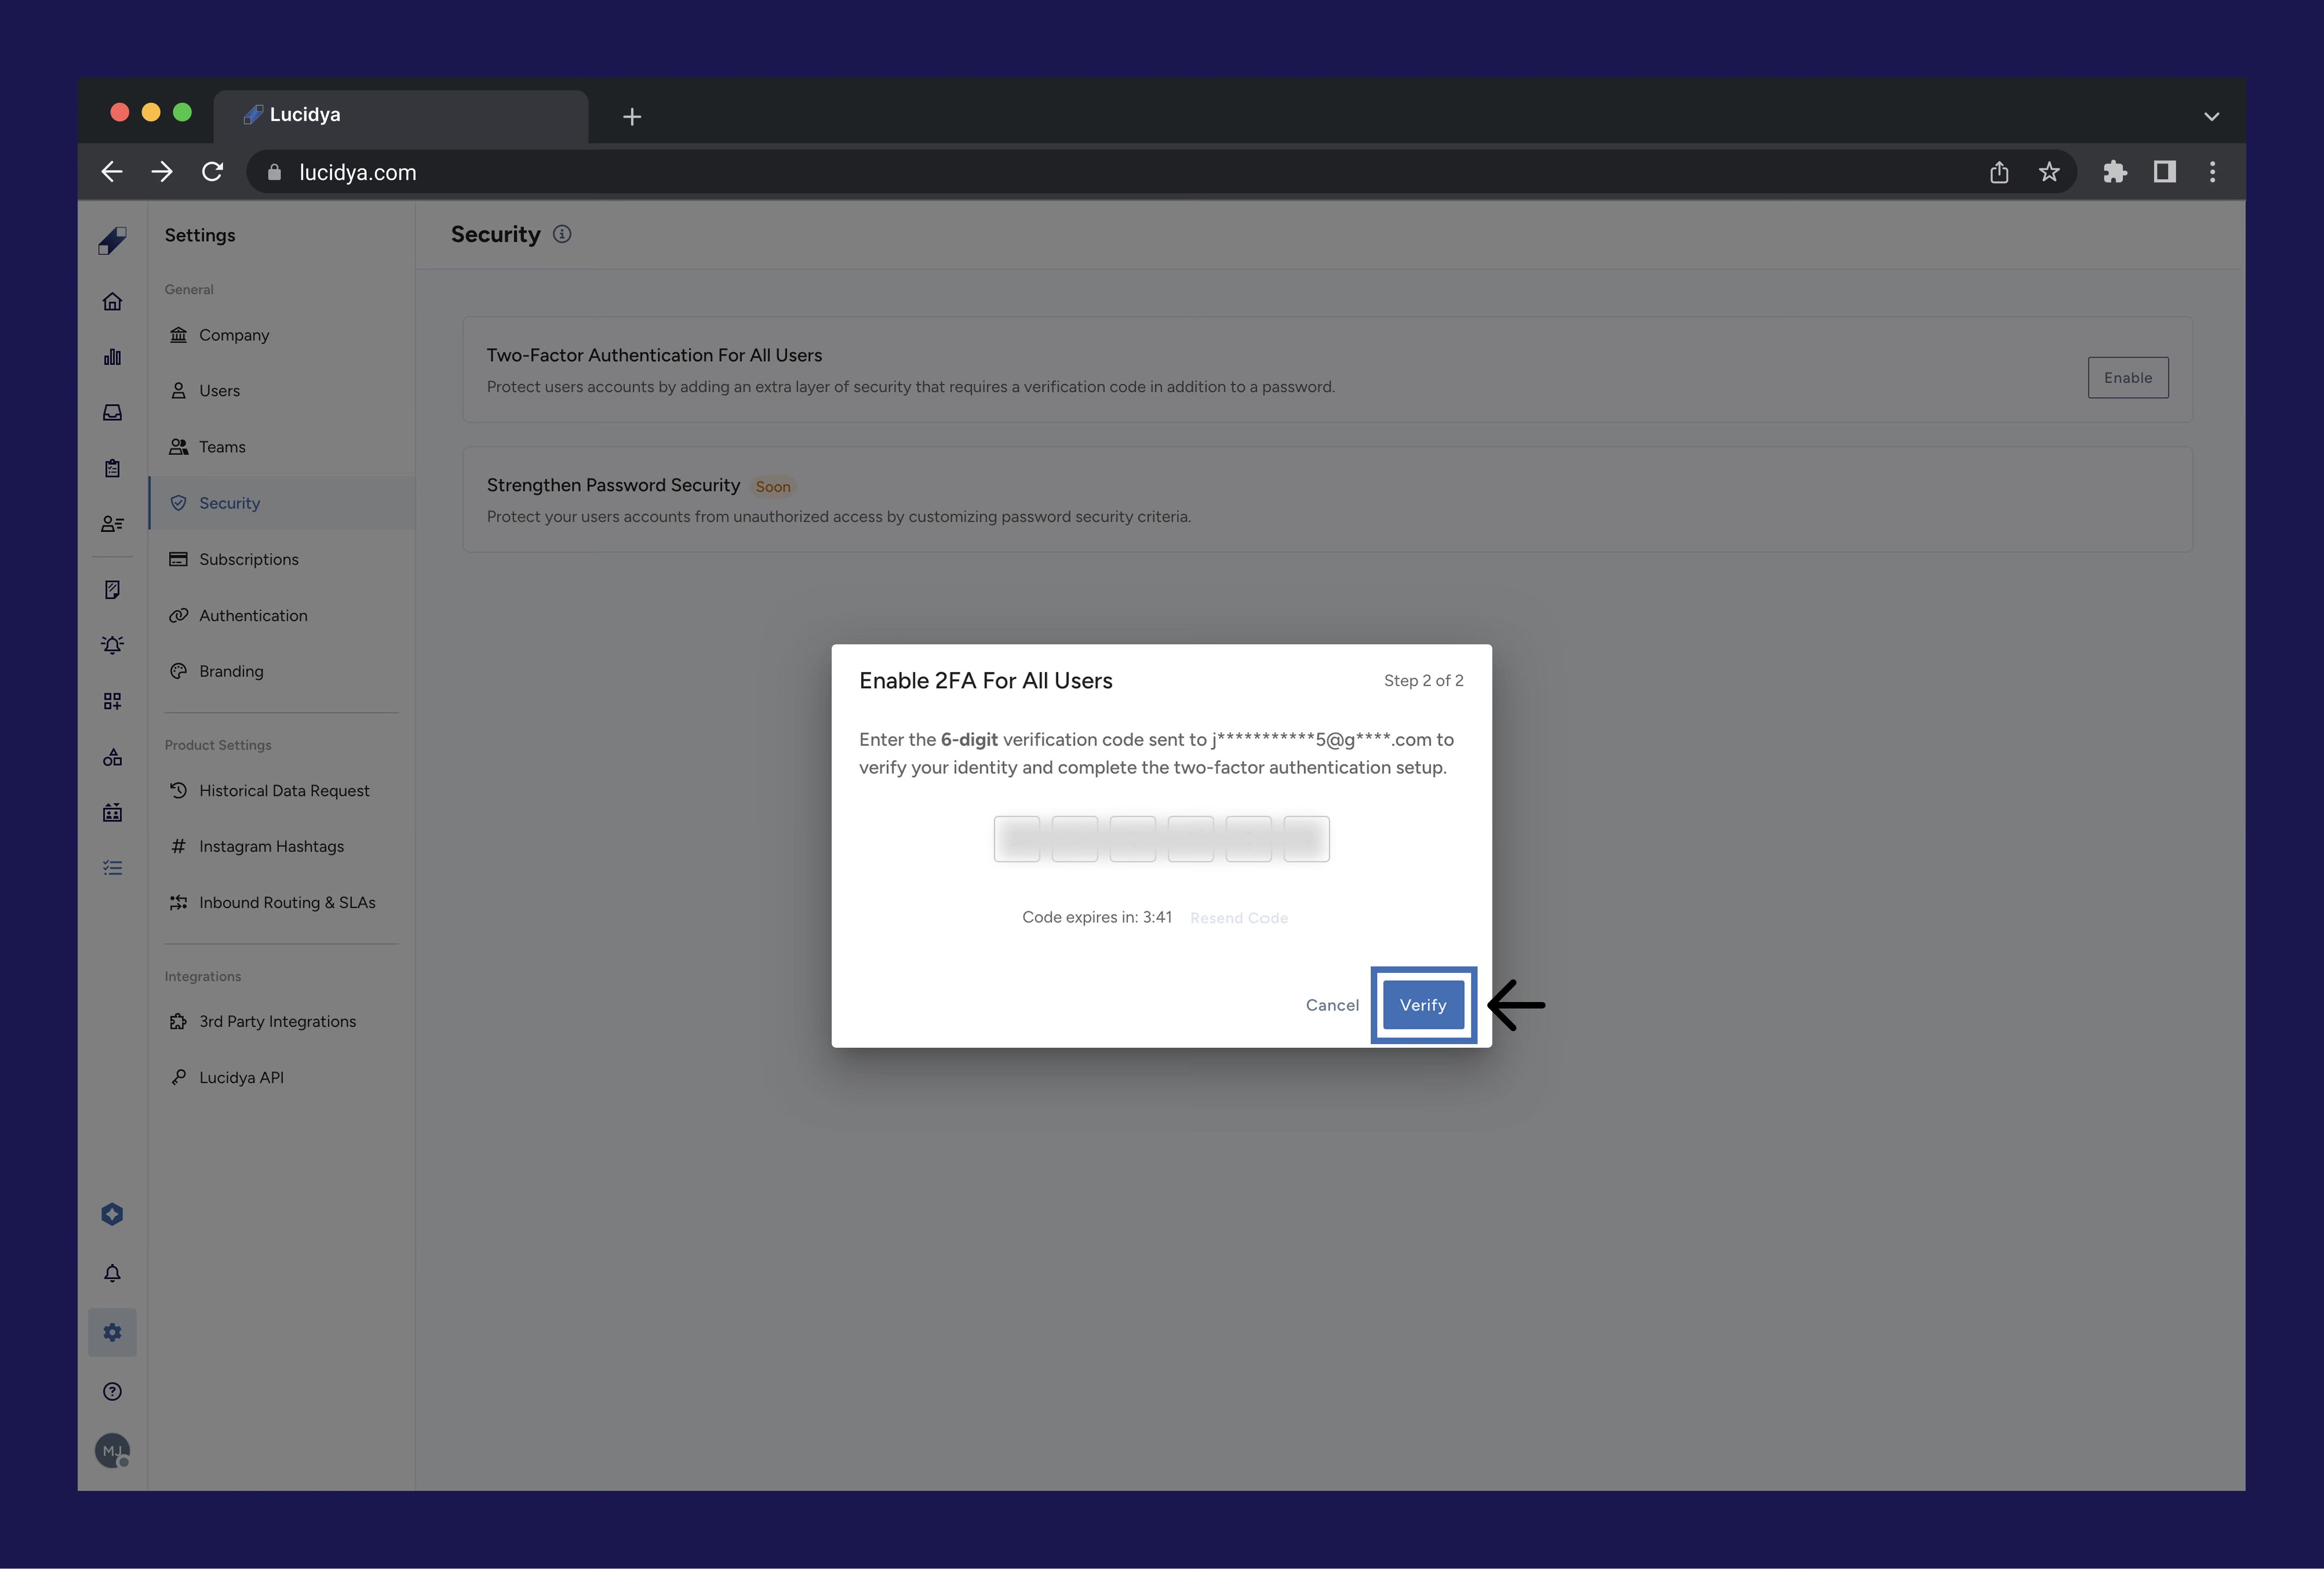
- You will receive an email with a verification code.
- Copy the code, enter it in the verification field, and click Verify.
- You have 5 attempts to enter the code correctly. After 5 failed attempts, the Enable button is temporarily disabled and a retry tooltip appears.
- A success message will confirm that 2FA has been enabled.
All existing users will receive an email with setup instructions and will be required to complete 2FA setup at their next login. Active user sessions remain open but each user must set up 2FA when they next log in.
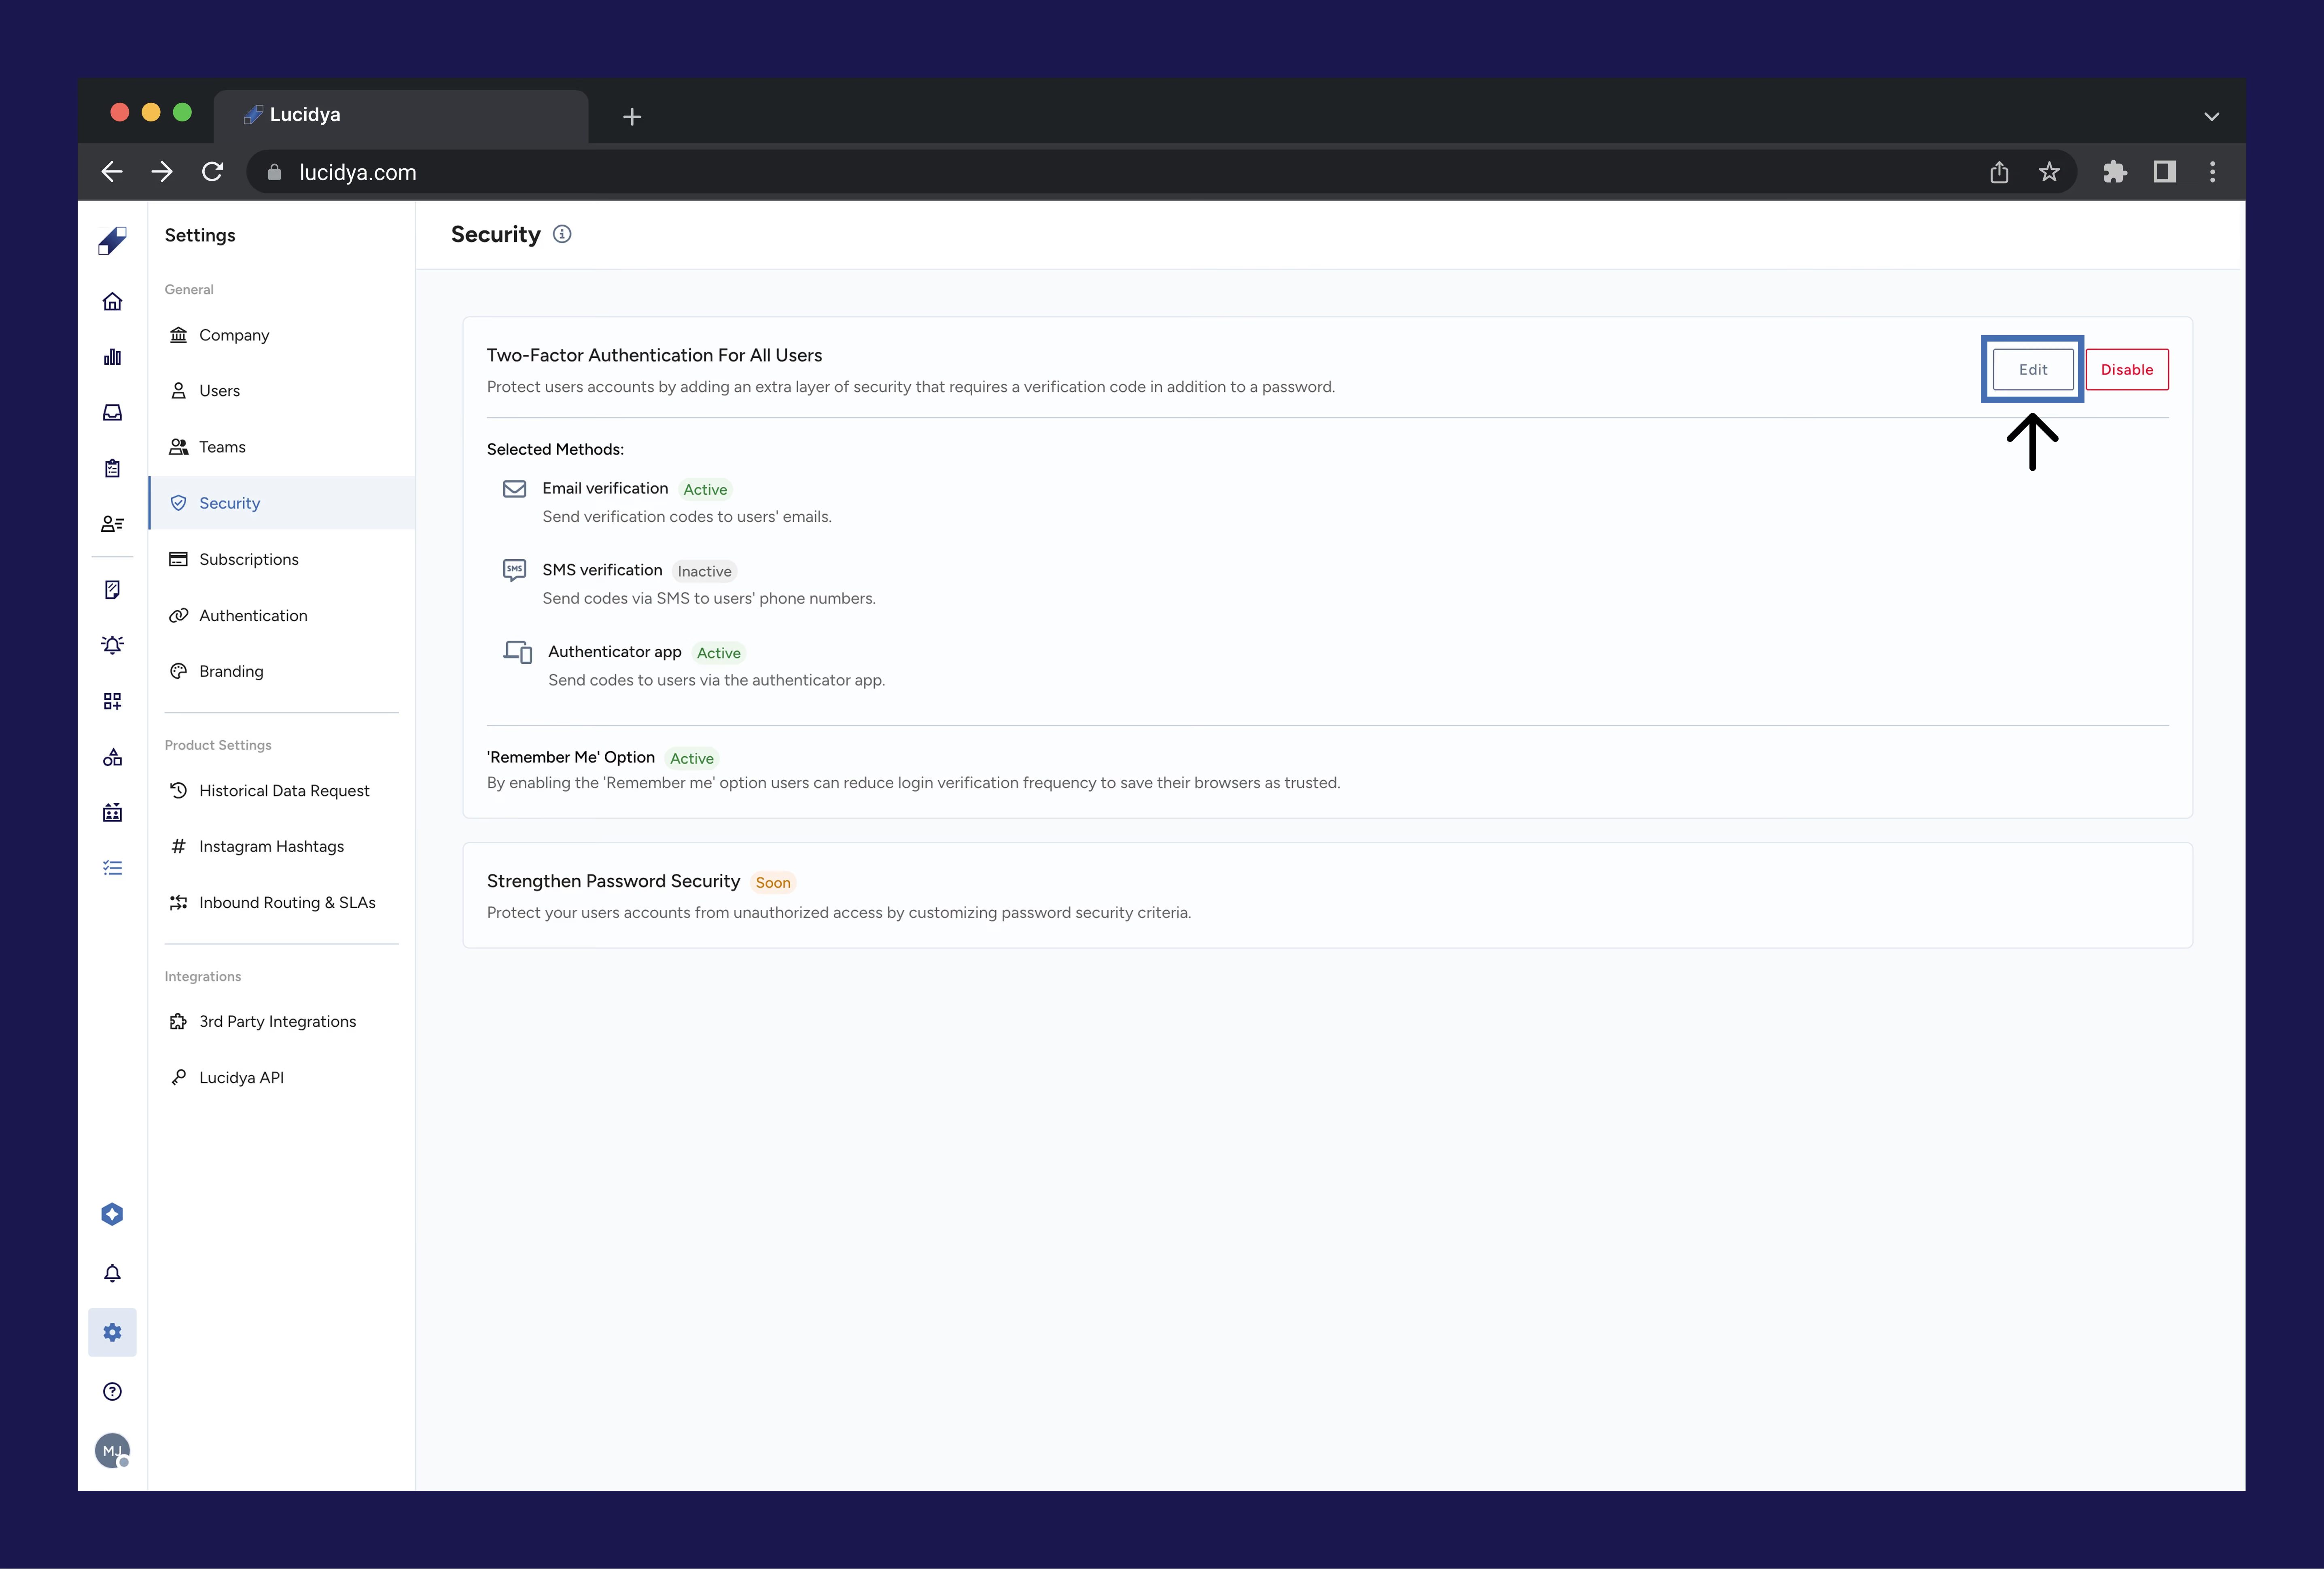
The Security tab will now show a green Enabled label alongside Disable and Edit buttons.
Editing 2FA Settings
- Click the Edit button next to the Enabled label. What you can edit depends on your package. On standard packages (without SMS) you can only toggle Remember Device on or off. With the SMS package you can change verification methods and toggle Remember Device.
- At least one verification method must remain selected at all times. The Next Step button is inactive if no methods are selected.
- Enter the verification code sent to your email to confirm the changes.
- You have 5 attempts. After 5 failed attempts the Disable and Edit buttons are temporarily disabled with a retry tooltip.
- A green confirmation message confirms the update was saved.
Disabling 2FA
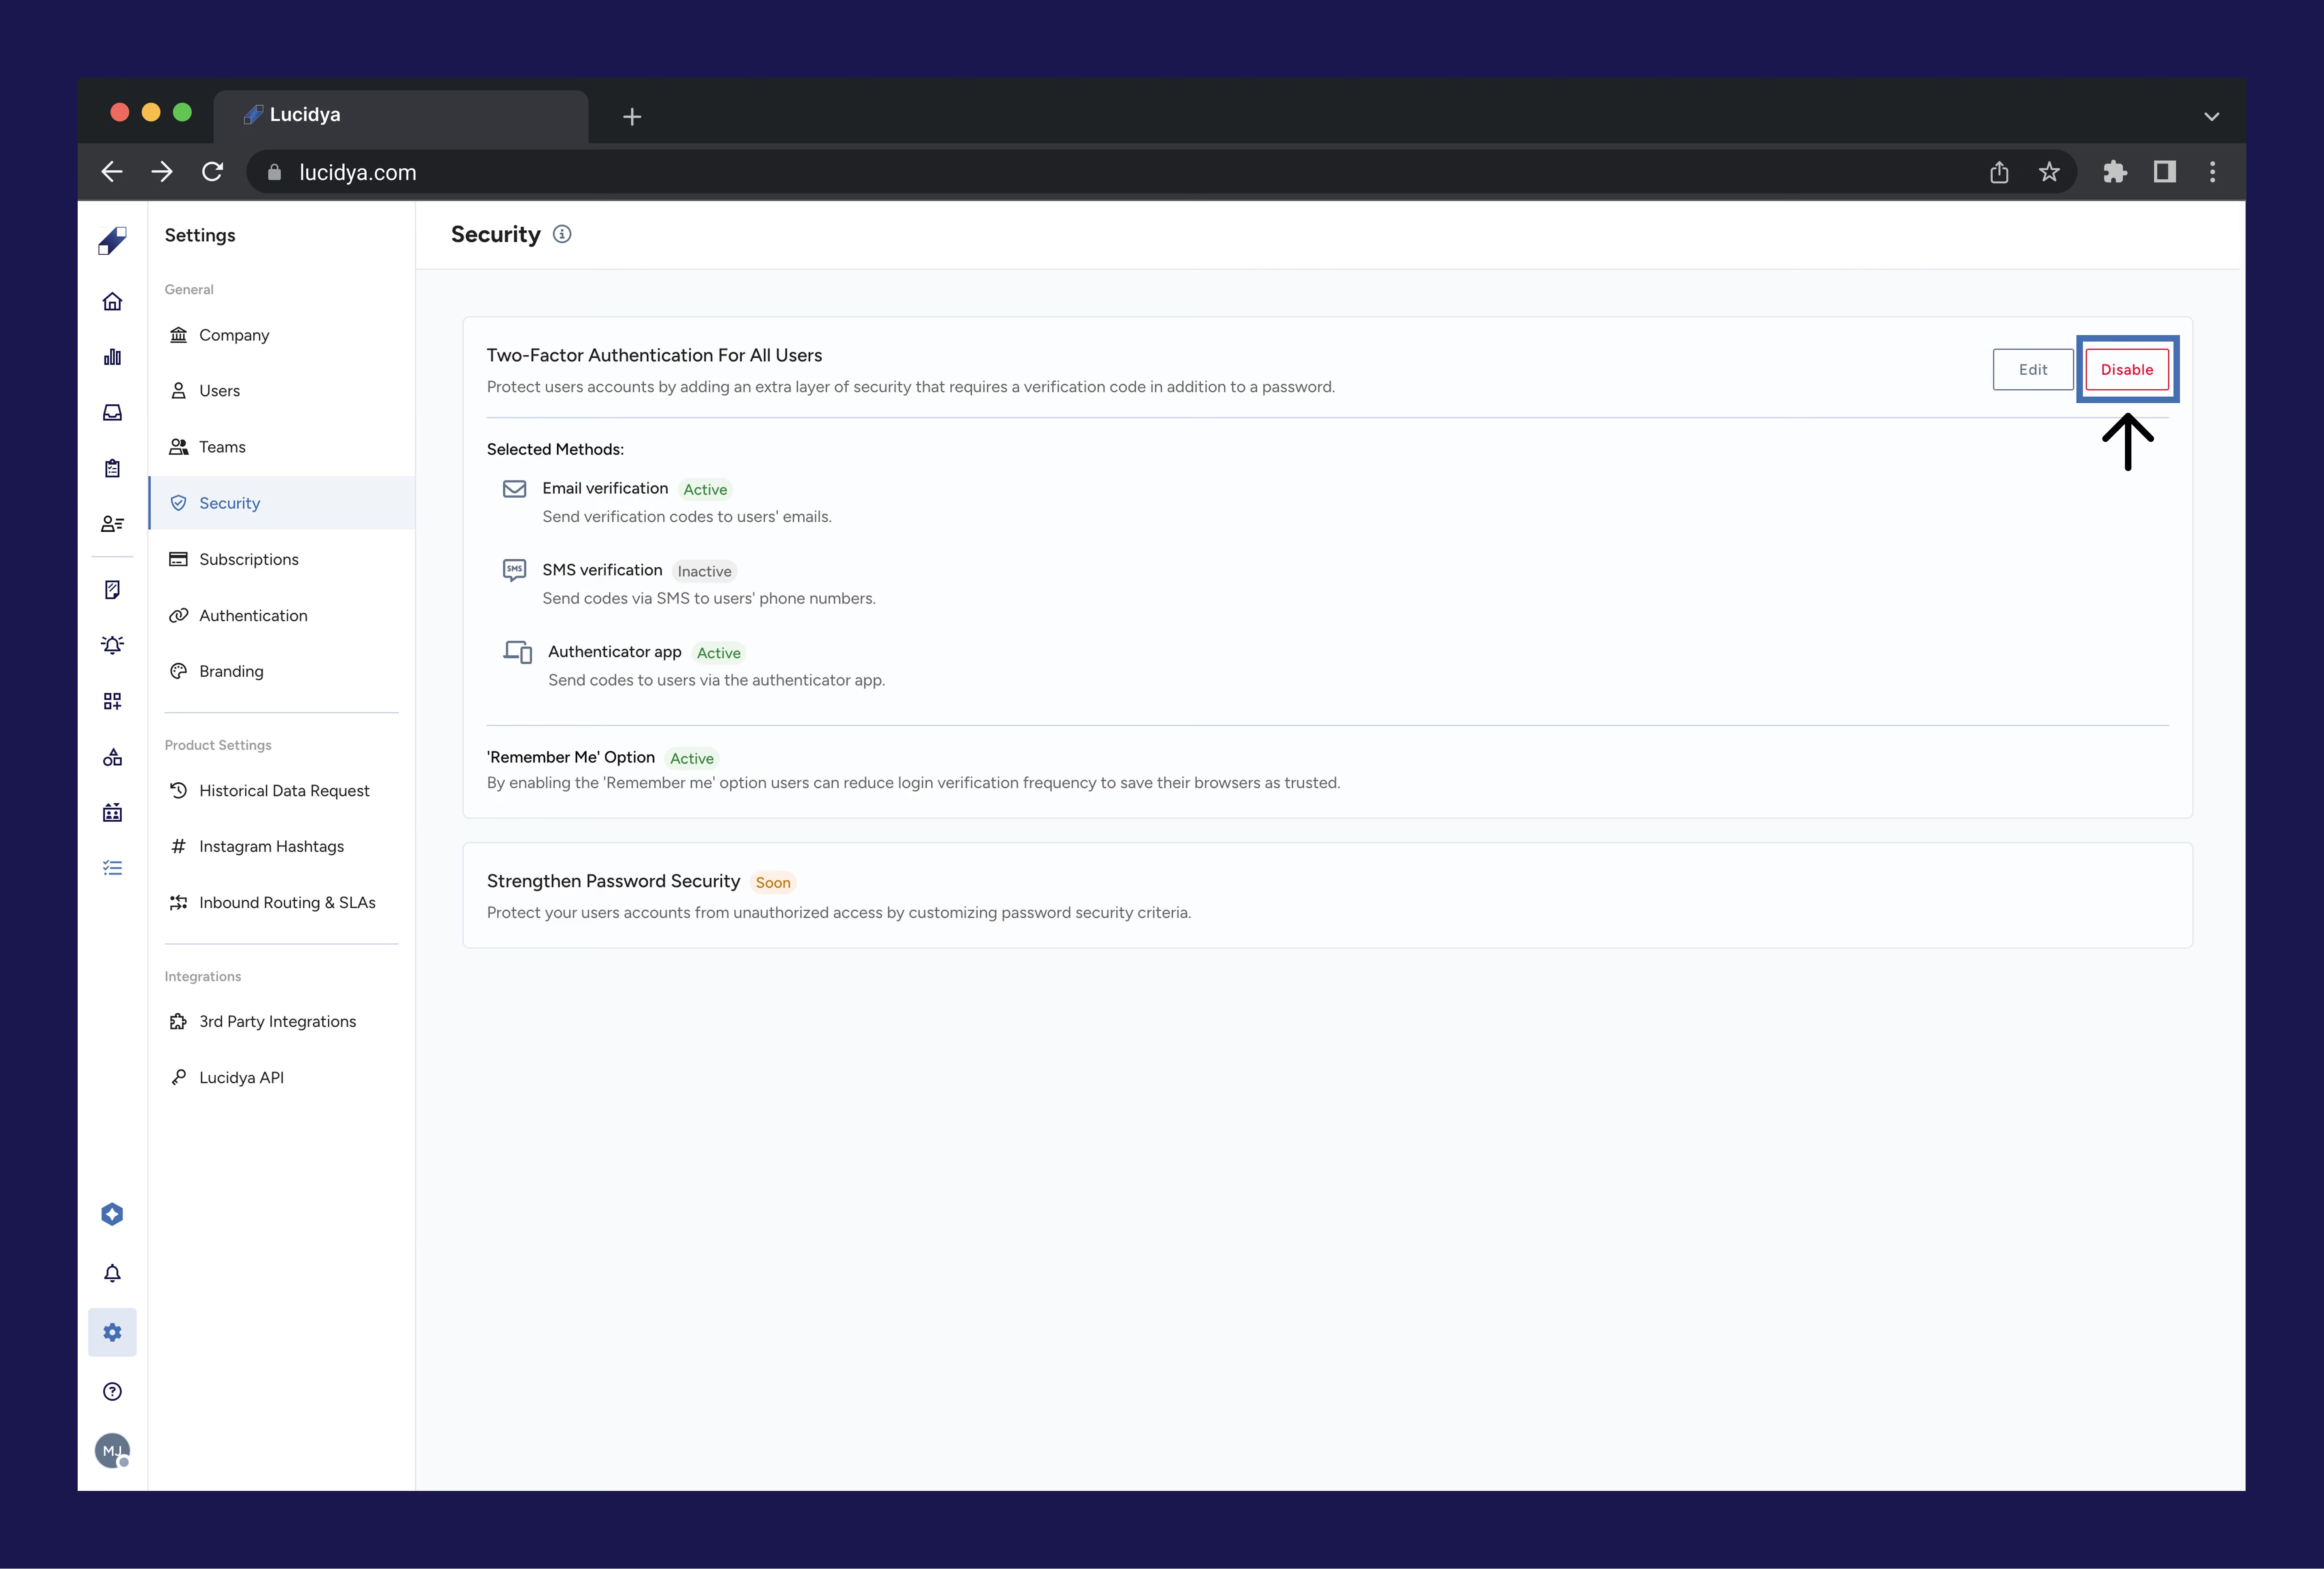
- Click the Disable button and confirm the action in the popup.
- Enter the verification code sent to your admin email.
- You have 5 attempts. After 5 failed attempts the Disable and Edit buttons are temporarily disabled with a retry tooltip.
- Once disabled, the Disable and Edit buttons are replaced with the Enable button and the Enabled label is removed.
Disabling 2FA is not recommended as it removes an important security layer. Note that disabling 2FA resets all user 2FA setups across the organization, including any individual configurations users had set up at the profile level.
For further assistance contact Lucidya Support.
Frequently asked questions
Yes. Once enabled, every user in your organization must complete 2FA setup at their next login. Individual users cannot opt out.
Users can choose from the methods you have enabled as an administrator. If you enable multiple methods, users select their preferred option during setup.
Existing authenticated sessions remain open. Users will receive an email prompting them to log in again and set up their 2FA method at their next login.
No. SMS verification is a paid add-on that requires the SMS package. You can request it directly from the 2FA configuration popup by clicking the Request button next to the SMS option. Email verification and Authenticator App are available by default on all packages.
No. Only administrators with Manager permission for the General Settings module can disable or edit 2FA settings for the organization.
You have 5 attempts. After 5 failed attempts the relevant button (Enable, Disable, or Edit) is temporarily disabled and a retry tooltip appears. Your account is not locked.
Yes. Disabling 2FA resets all user 2FA configurations, including any setup users completed at the profile level.